Third-Party Governance · TPRM
Your entire third-party ecosystem, monitored continuously
Third parties are involved in 48% of data breaches (Verizon DBIR 2026), yet most programs assess only the critical ones, and only at onboarding. Verta covers the entire ecosystem, with AI analyzing the evidence.
- Who it's for
- CRO, Compliance, GRC and Procurement
- Replaces
- Spreadsheets, manual questionnaires and dollar-priced platforms
- Starts with
- A proof of value with one group of third parties and the regulation that matters most today
What changes
Your third-party policy becomes configuration, and the team handles the exceptions
Coverage of the entire ecosystem, monitoring throughout the contract and criteria set by your policy, with an audit trail from the very first interaction.
-
One questionnaire
A single questionnaire produces reports for multiple regulations at once.
-
AI-analyzed evidence
Seven dimensions of analysis, sorted into approve, review and reject bands that your policy defines.
-
Three tiers of requirements
Critical, intermediate and basic: rigor proportional to risk, without overwhelming smaller suppliers.
-
Escalating follow-ups
From a gentle reminder to an invoice-hold notice, all tracked on the dashboard.
-
Action plan and mirror effect
The third party sees its own risk and improves through a phased plan.
How it works
From onboarding to monitoring, with no spreadsheet in between
- 01
Register
Third parties by company tax ID (CNPJ), with the criticality of each contract.
- 02
Assess
One questionnaire, with AI analyzing every piece of evidence.
- 03
Classify
Maturity and risk scores for your business, in tiers.
- 04
Treat
Action plans, follow-ups and, for critical suppliers, cyber insurance.
- 05
Reassess
Cycles in which the third party answers only what has changed.
The platform in action
Your entire ecosystem on one screen, each third party in depth
From the program dashboard to the detail of each third party: impact, contract, exposed credentials and attack surface, all in the same record.
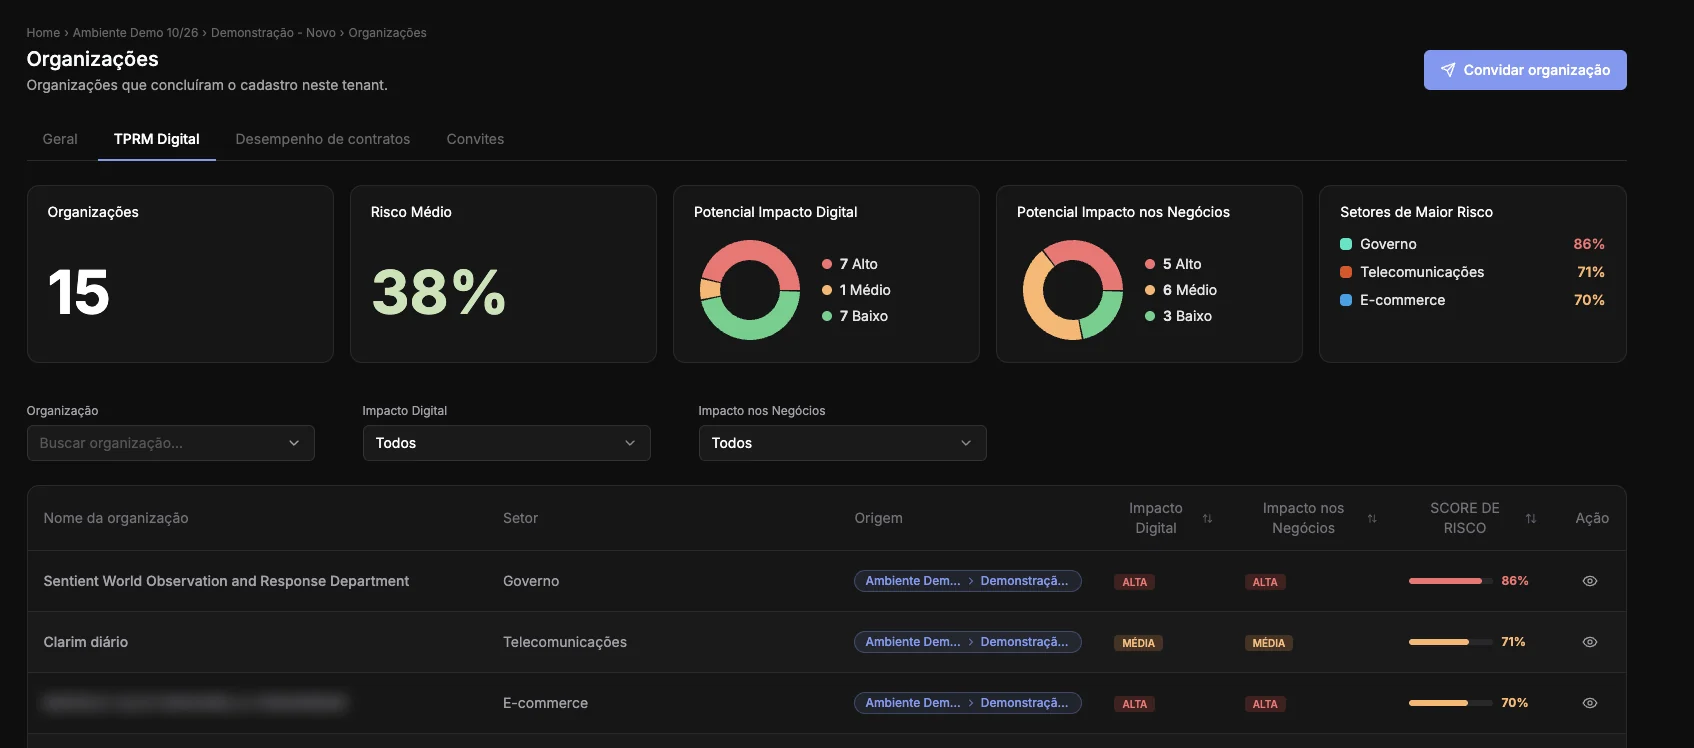
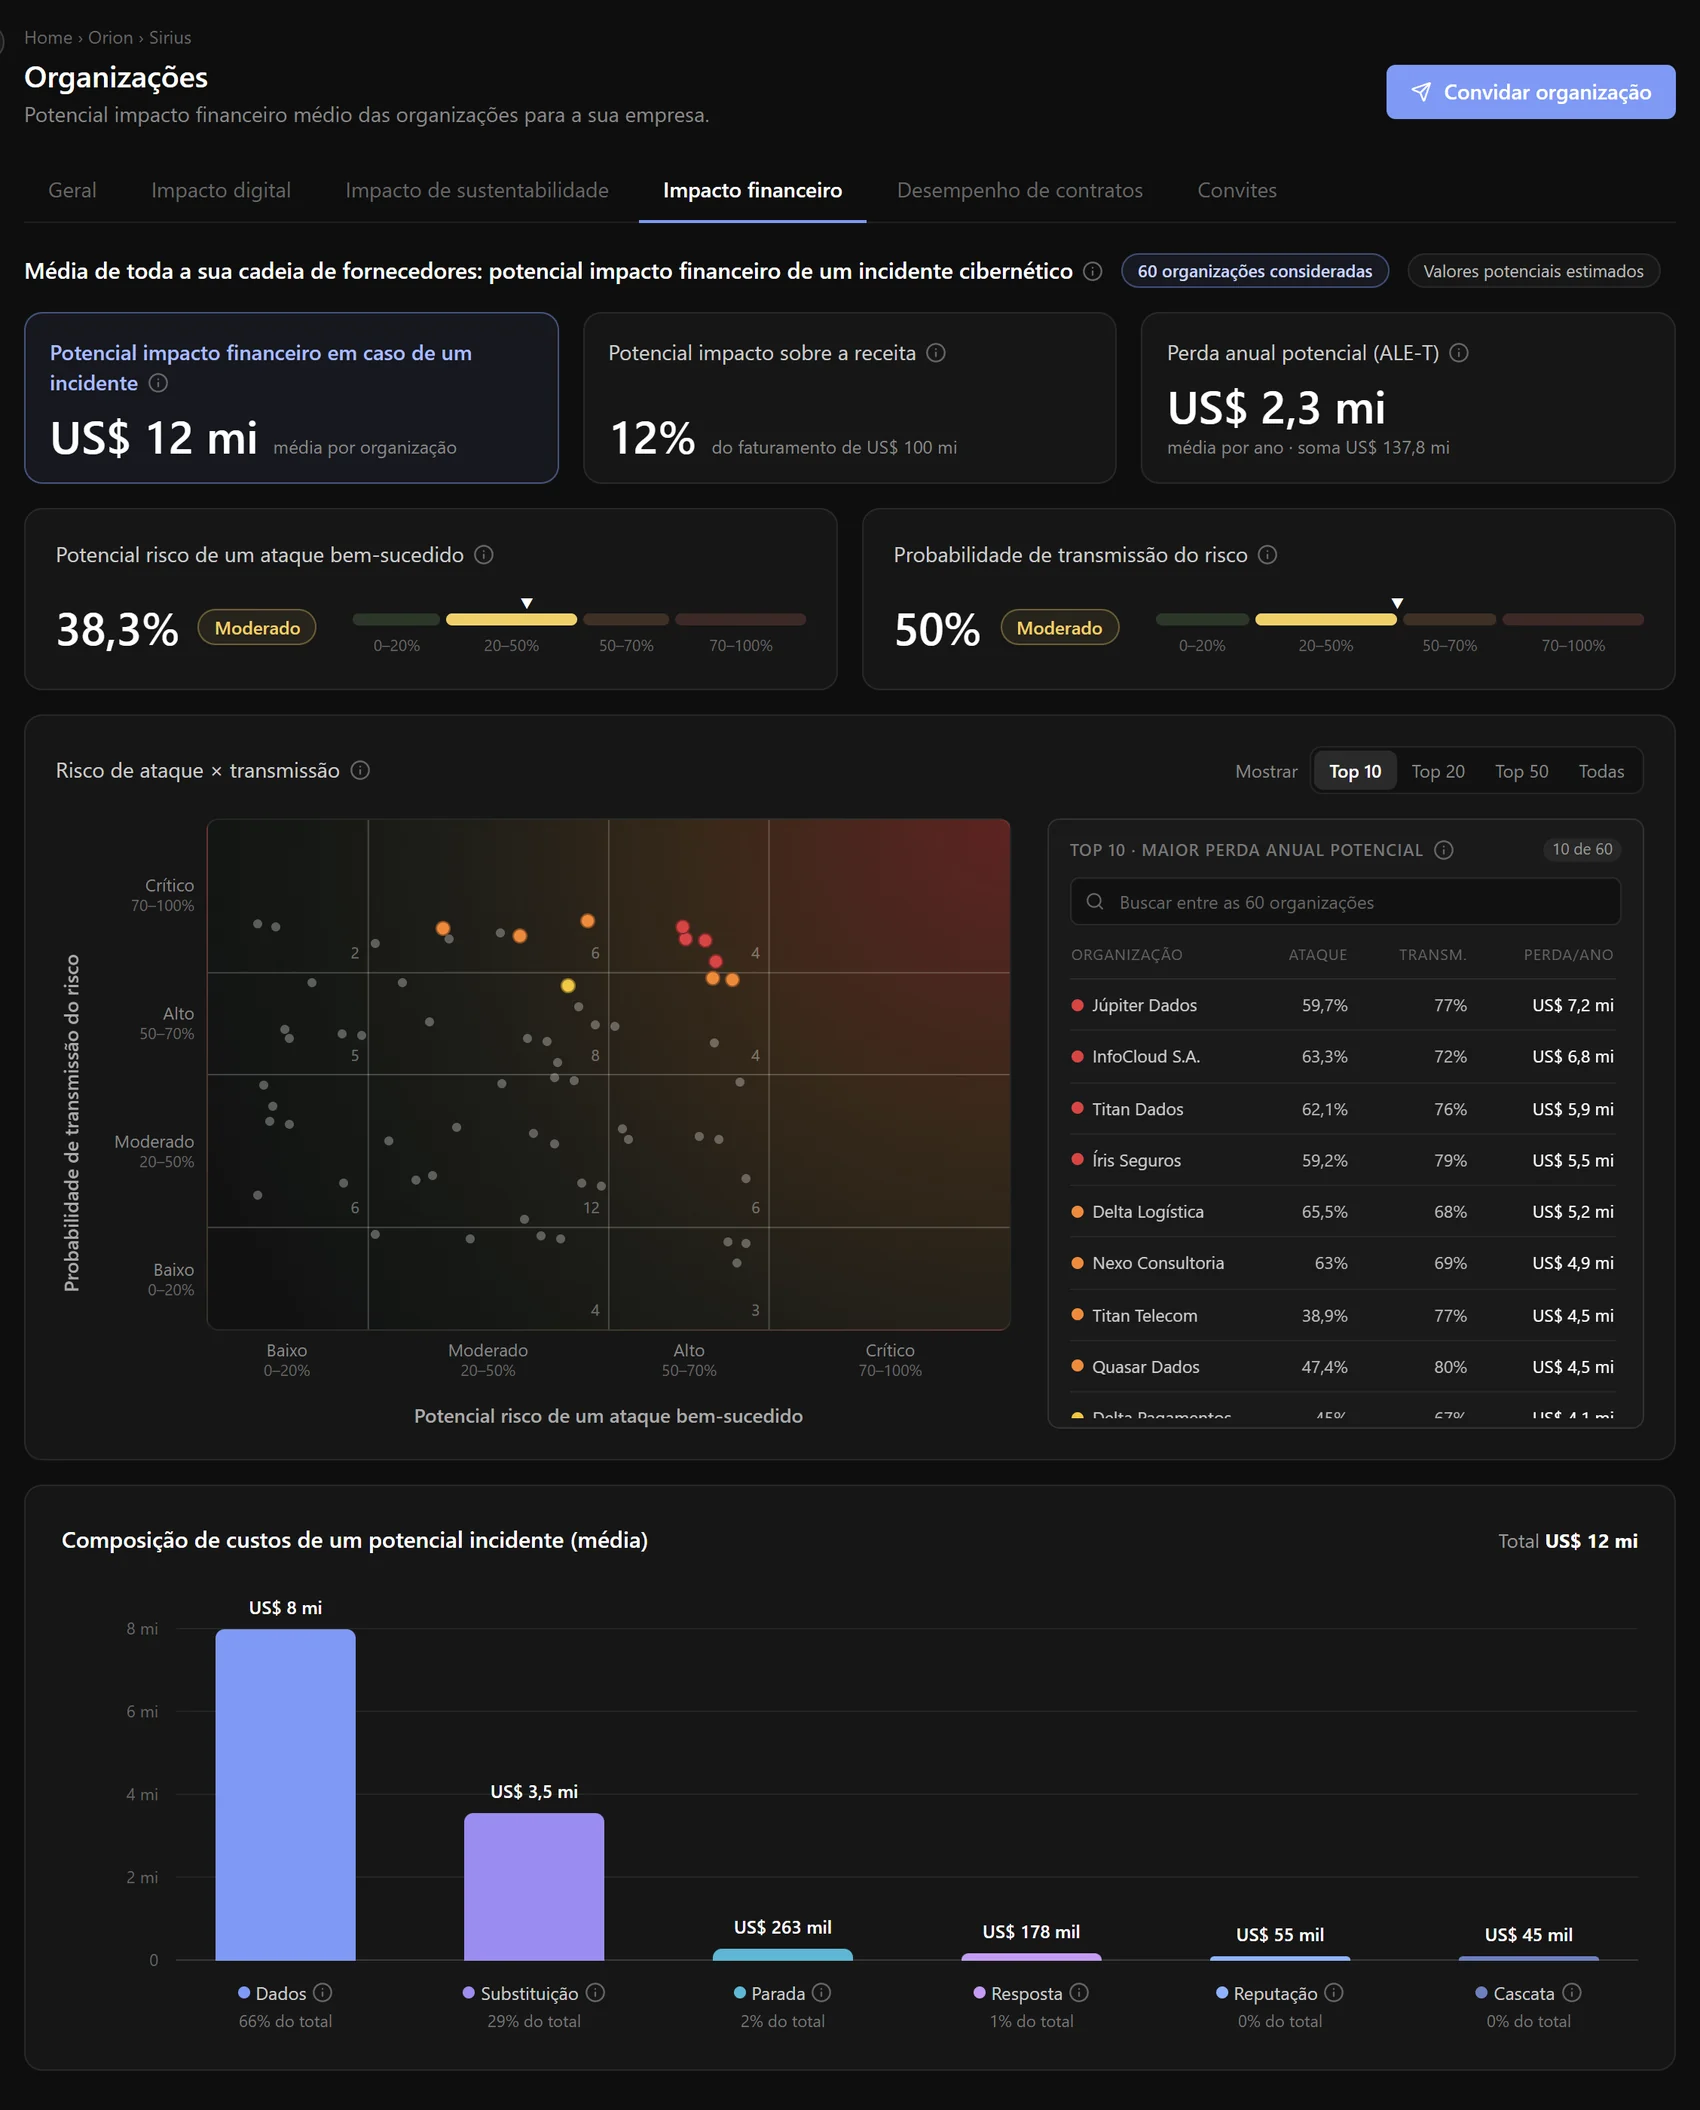
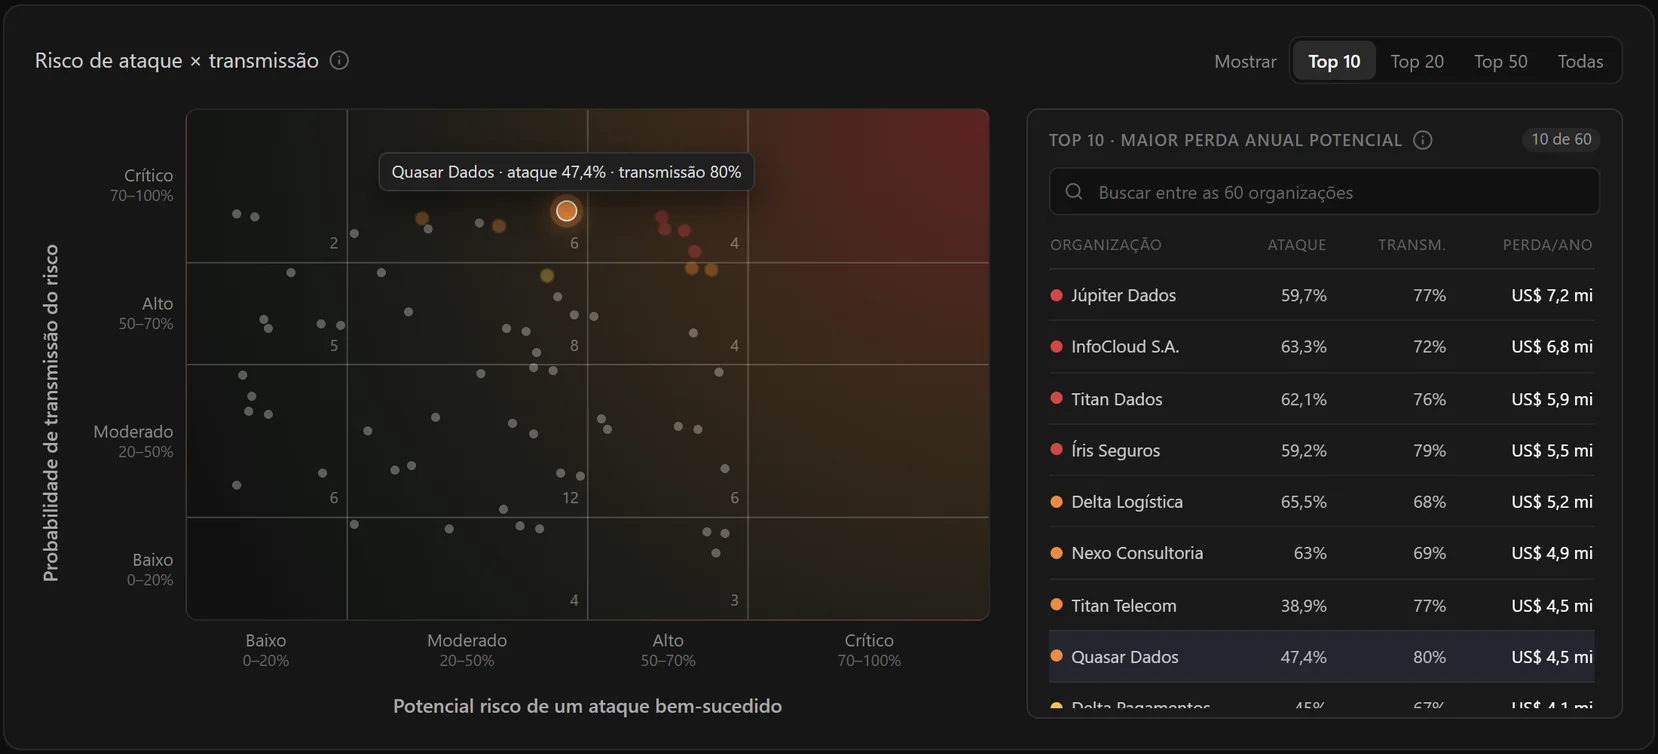
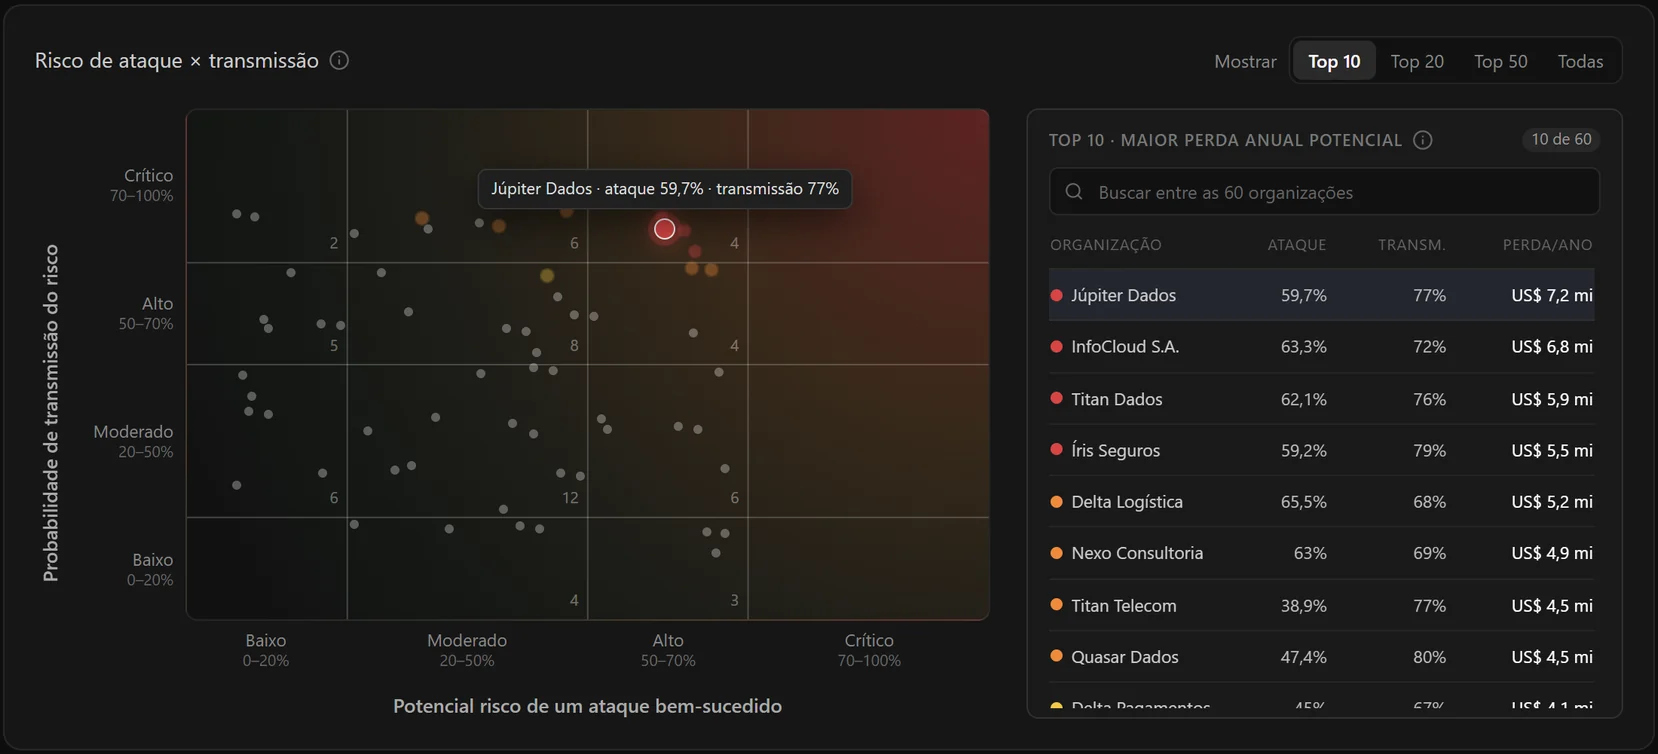
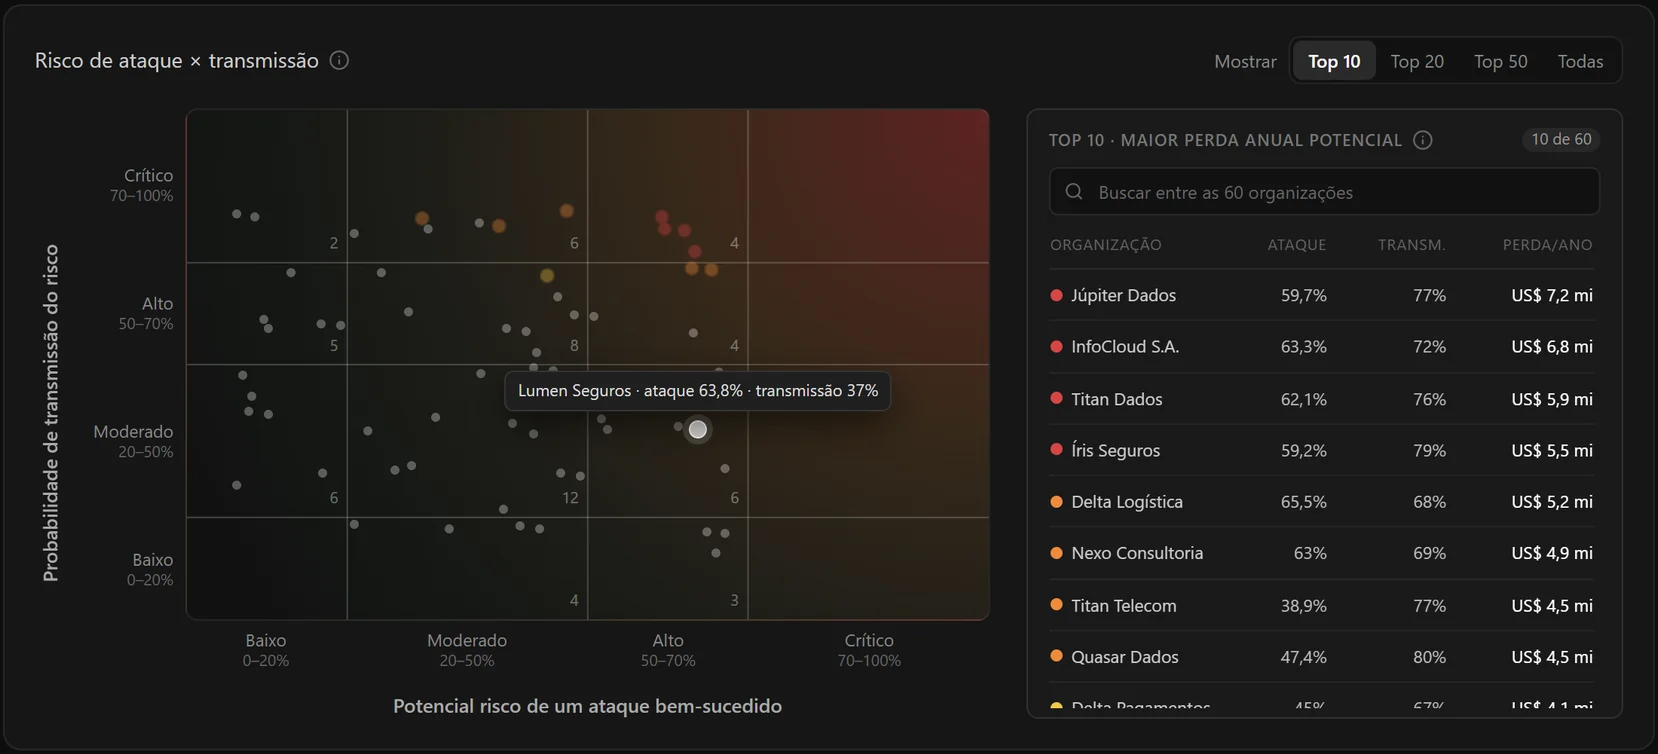
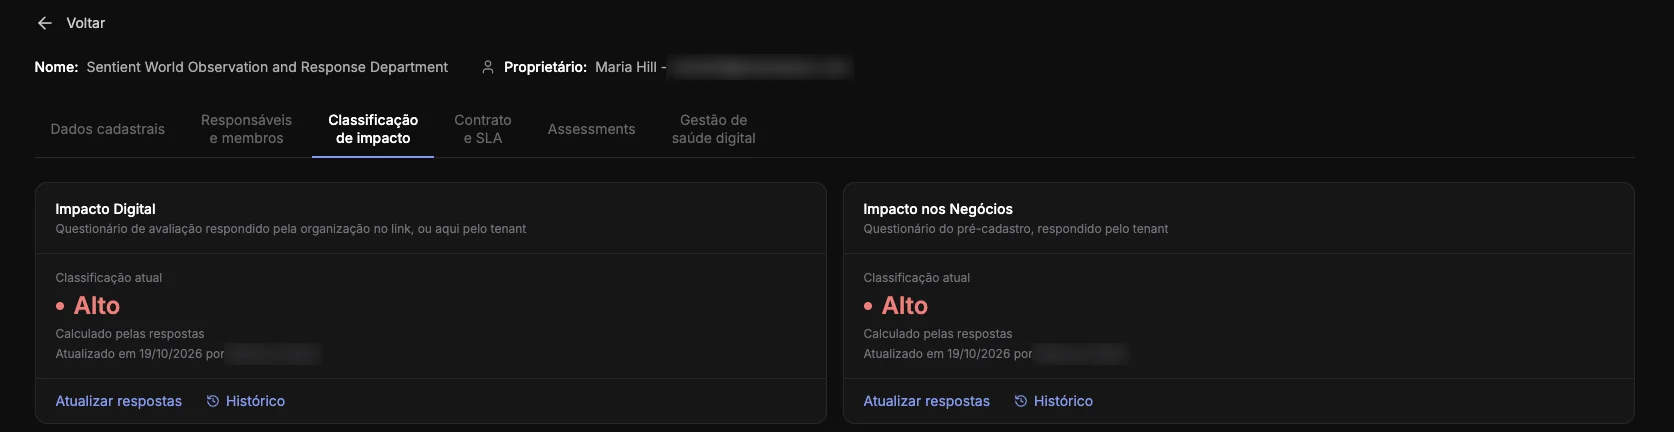
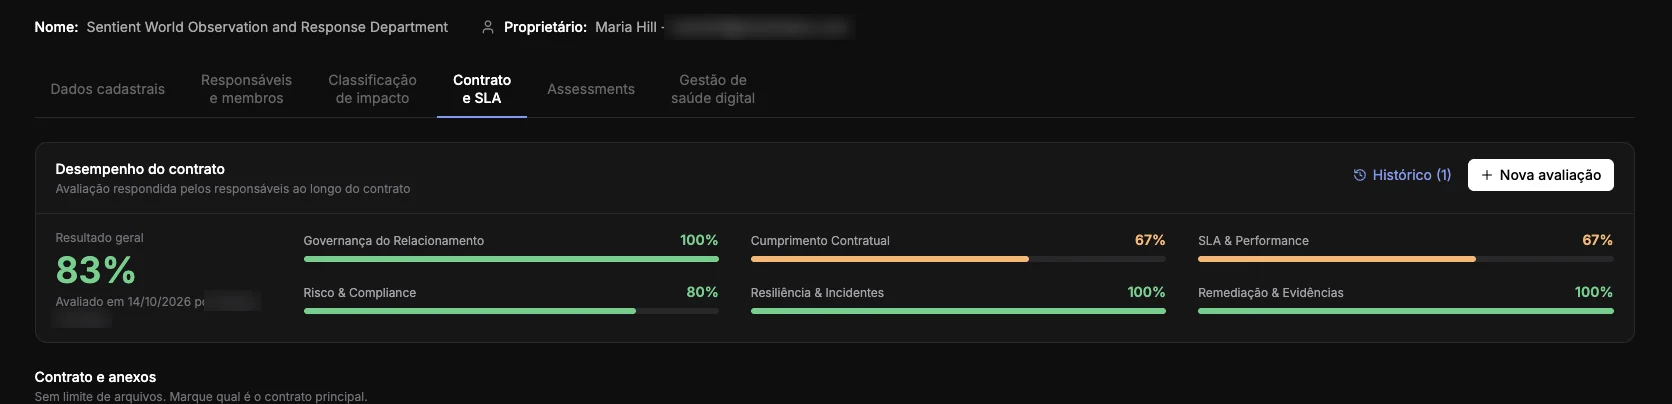
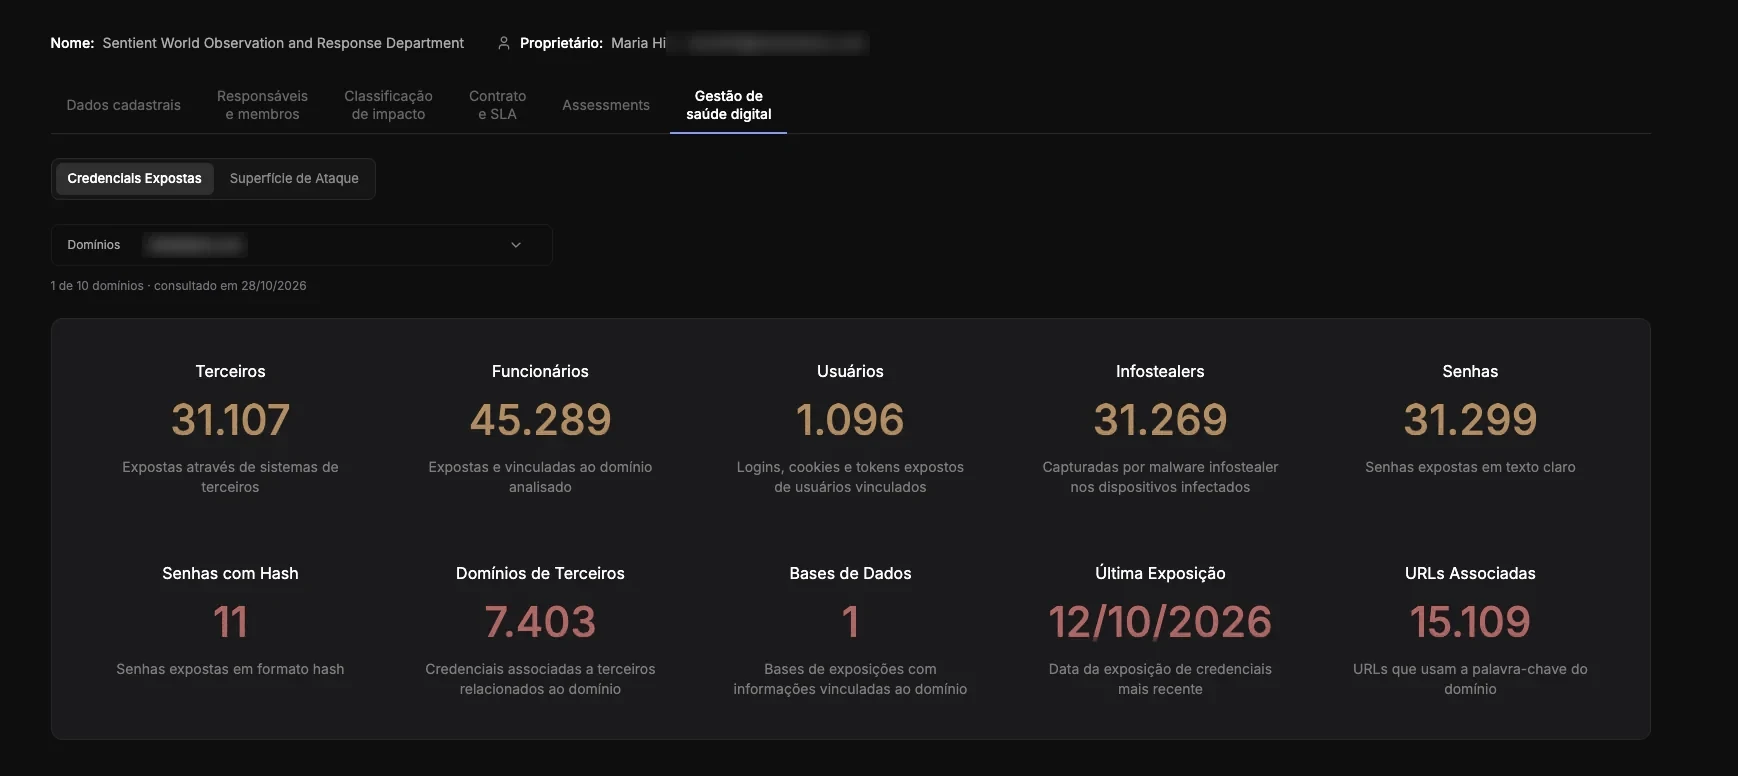
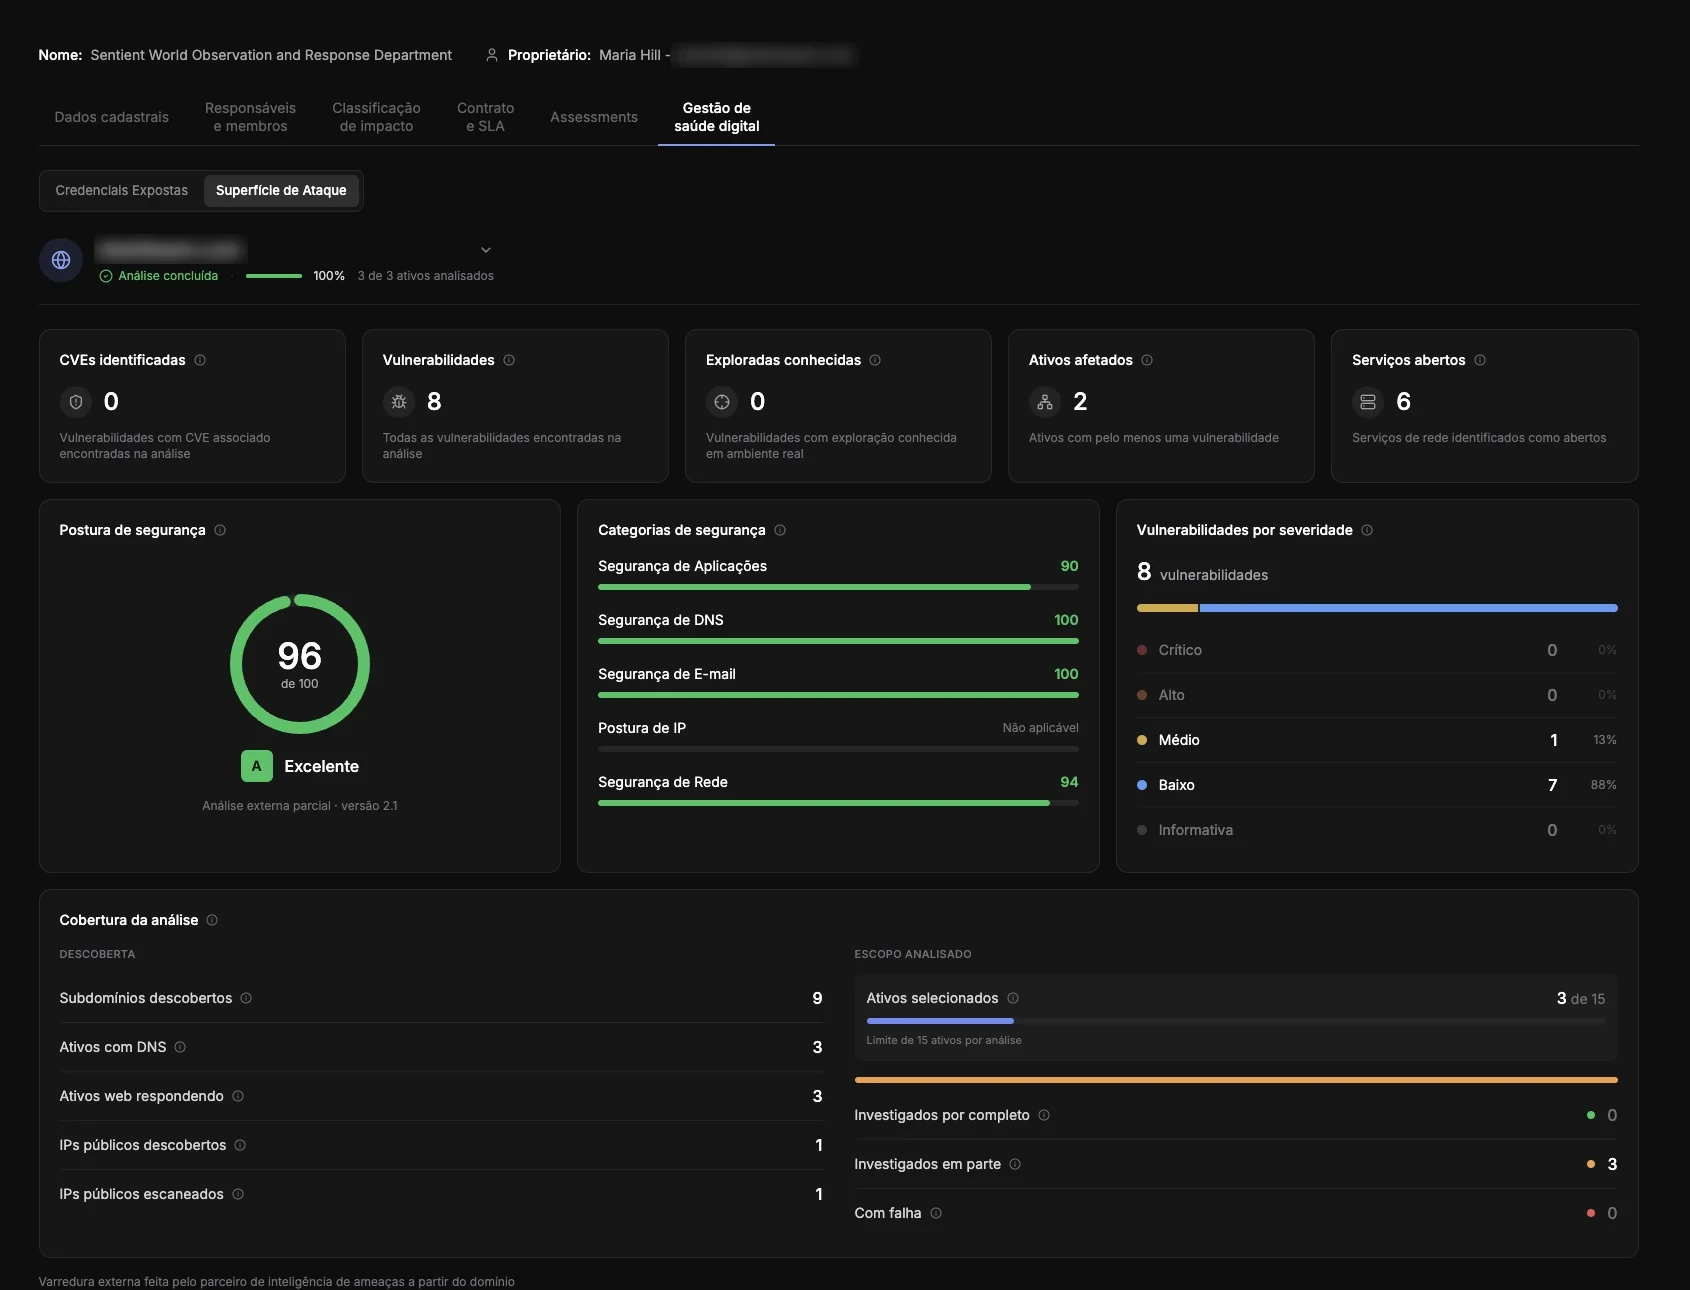
Screens from the demo environment. Names of people, e-mails, tax IDs and domains have been hidden.
Measured results
At one of the country's largest banks, the third-party program scaled up
Two steps stay human by choice: classification by the business and approval of the exceptions that go to committee.
- 11 of 13 steps automated
- 87% less analysis time
- 44x more assessments per year
A self-sustaining program
Third-party governance stops being a cost center
-
The ecosystem funds the program
Responding to the assessment is a program requirement, and the cost can be passed on to the ecosystem, with subsidized benefits for the third party.
-
Insurance for critical suppliers
The program can require a policy from critical third parties; those without one can buy it on the platform itself, through Akad Seguros.
-
Priced in reais
A platform that goes live in weeks, with no heavy implementation and no dollar-denominated contract.
Connects the other domains
The full view of each third party: who they are, how exposed they are, what they access and whether they're insured
Digital Governance
Digital Health for each third party
Exposed credentials and attack surface feed the program score.
Access
Access through the secure browser
An approved third party enters your environment without ever knowing the credential.
Corporate & Compliance
Your group on the same base
Companies within your own group assessed by tax ID (CNPJ), under shared governance.
Next step